Bug #8
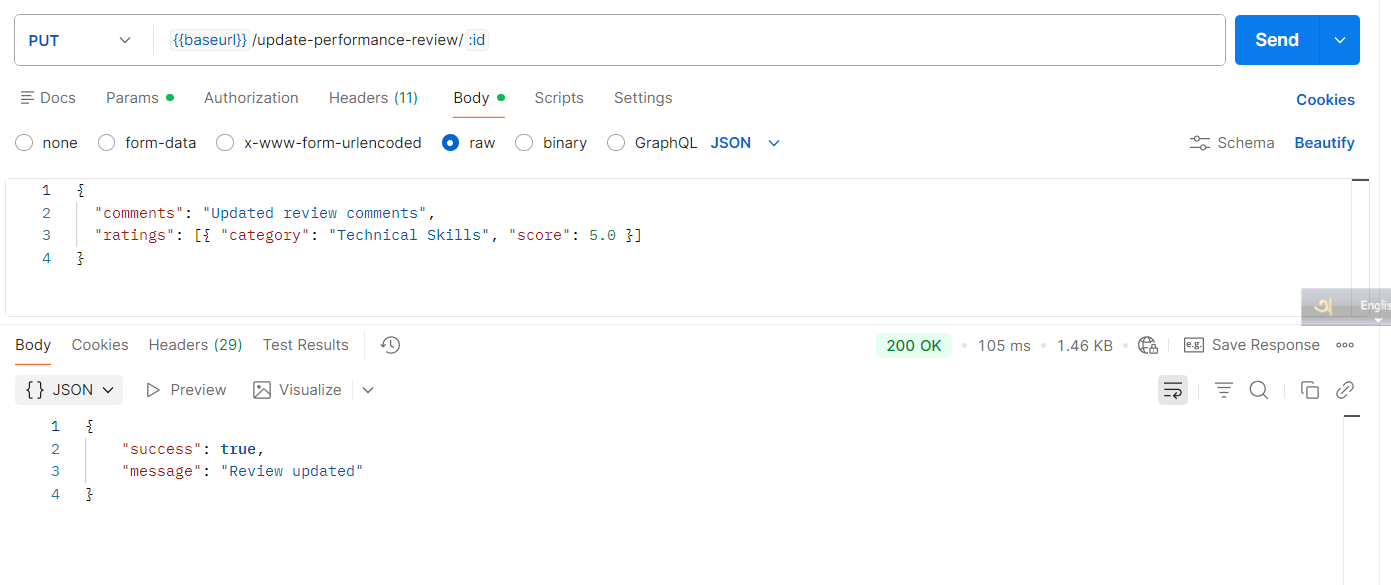
openEmployee can update another employee's performance review (PUT /update-performance-review/:id)
0%
Description
The /update-performance-review/:id endpoint has no ownership or role check before applying an update. It only verifies that the request carries a valid JWT — it does not confirm that the caller is the original reviewer, a manager of the reviewed employee, or holds any elevated role.
Because of this, a regular Employee can locate or guess any performance review's ID and directly modify its contents — ratings, comments, and overall score — even though they had no part in creating that review. This is exploitable both through the app UI (if the review ID is exposed anywhere in the frontend, e.g. in an API response or URL) and directly via a tool like Postman, since the endpoint itself performs no authorization check regardless of how the request is sent.
This allows any employee to alter or sabotage a colleague's official performance record after the fact — inflating their own score, lowering someone else's, or erasing a manager's original comments — with no audit trail distinguishing a legitimate reviewer's edit from an unauthorized one.
Files